Linux Notes: SSL, TLS, OpenSSL
- The information presented here is intended for educational use by qualified computer technologists.
- The information presented here is provided free of charge, as-is, with no warranty of any kind.
(a simple) Introduction to SSL/TLS for Linux people
The name game
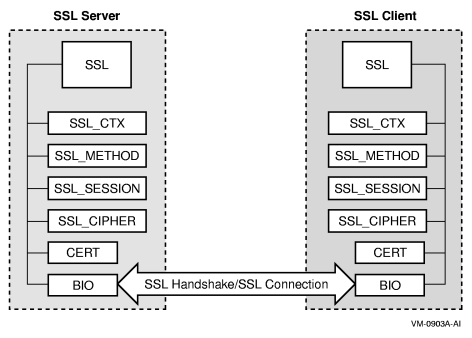
- SSL (secure sockets layer) is a
communication protocol developed by Netscape Communications and RSA Data Security to add privacy and security to internet
communications. Today's financial transactions over the web depend upon this technology.
- Public-key cryptography
- original work by Whitfield Diffie, Martin Hellman, and Ralph Merkle (three Stanford academics) was done in 1976.
- Diffie-Hellman key exchange is used to obscure the remainder of the SSL handshake
- click here to play with my Diffie-Hellman demo
- original work by RSA (three MIT academics: Ron Rivest, Adi Shamir and Leonard Adleman) was done in 1977 but wasn't publicly described until 1995 during the creation of VeriSign
- much was cobbled together by Taher Elgamal who was then working at Netscape
- The first browser to employ SSL (Secure Sockets Layer) was Netscape Navigator 1.1 in March 1995)
- The first browser to employ SSL (Secure Sockets Layer) was Netscape Navigator 1.1 in March 1995)
- Versions:
- SSLv1 (a.k.a. SSL1 and SSL-1) was a proof-of-concept which was never released
- SSLv2 (a.k.a. SSL2 and SSL-2.0) was released in 1995 and considered by many to be a work in progress. For example, it does not support client authentication
- SSLv3 (a.k.a. SSL3 and SSL-3.0) was released in 1996 and adds support for client authentication as well as additional ciphers
- TLSv1.0 (a.k.a. TLS 1.0) was released in 1999. This fourth revision
was so important that the name was changed to TLS (transport
layer security) even though many people today think of TLSv1.0 as SSLv4 if not SSLv3.1. From a programmer's view, some of the API
labels and data structures were changed. This was done so new SSL applications are unable to accidentally link to older SSL libraries. The new TLS stack supports
older SSL protocols (if enabled) which are implemented with newer code
A few more details:- The main reason for changing the API begins with an unintentional security bug. Before the sale of Netscape to AOL in 1999, Netscape published much of their source code into the Mozilla Project (an open source software site). A short time later, a paranoid programmer at company name deleted modified the SSL library so it would would execute a random number function three additional times during key generation. Apparently, the programmer inadvertently used a 32-bit variable rather than a 64-bit variable which had the unintended effect of reducing the effective key size by 50% while reducing the effective key space by 75%. This code was then published through the Mozilla Project and no one knows how much of it escaped into the wild. Shortly after the revelation, many software publishers quickly realized it was better to introduce security changes cooperatively through the IETF (Internet Engineering Task Force) where more eyes get to see the code before it is published. The TLS stack represents the efforts of IETF (e.g. TLS is an IETF standards track protocol)
- The aforementioned bug may not be as obvious as you may might think. Remember that everything in the API was originally written in C which is the only truly
portable computer programming language. Rumor has it that the programmer who broke SSL declared "a 32-bit variable" thinking it was "a 64-bit variable on his
system" so it's a classic case of the computer doing exactly as it was told.
As HAL-9000 once said: "This sort of thing has cropped up before, and it has always been due to human error".
I am not sure if the programmer "thought long meant 64-bit because he was on a native 64-bit architecture" or "was unaware of the fact that long long is required to declare a 64-bit variable". This is why the IETF changed the type of that variable to uint64_t (unsigned integer 64-bit) which is now the source of much frustration as new programmers learn the c language. - I have always thought that long long was a really dumb idea for a number of reasons with the main one being that you would need to know that the mainframe definition of long meant 32-bit while word meant 16-bit. How many programmers have encountered the terms quadword (64-bit) and octaword (128-bit)? So perhaps the IETF solution is the least confusing after all.
- TLSv1.1 (a.k.a. TLS 1.1) was released in 2006.
- TLSv1.2 (a.k.a. TLS 1.2) was released in 2008.
- TLSv1.3 (a.k.a. TLS 1.3) was released in 2018.
- Some computer professionals have commented that this protocol has changed significantly so should be relabeled TLSv2.0
- Some computer professionals have commented that this protocol has changed significantly so should be relabeled TLSv2.0
- SSL/TLS is now used in numerous other places like:
- communicating securely with a POP3 server over TCP port 995 (the default insecure port is 110)
- FTPS (FTP over SSL) which must not be confused with SFTP (FTP over SSH)
- Server authentication (mandatory) is one way that a client can ensure the server is who it claims to be.
- Client authentication (optional) is one way that a server can ensure the client system is who it claims to be. In the early days of e-commerce, a credit card was
thought to be the only necessary piece of client identification but how can you communicate securely without making a credit-card purchase?
- OpenSSL is (primarily) a C-language library used to implement:
- the Secure Socket Layer (SSL) protocol. This facilitates the implementation of SSL into software without needing to reinvent the wheel every time a developer needs to do so.
- a library of cryptographic functions meant to encrypt as well as decrypt. This means you do not need to set up an SSL connection in order to just use the cryptographic library
- a CLI (command line interface) tool for:
- testing library functionality (which can also be used as a training tool)
- testing SSL/TLS connectivity
- key generation
- certificate generation
- generating hashes
A 3-km (10,000 foot) overview of SSL
Overview
- Let's start by comparing an the opening of "an unencrypted web connection (http on port 80)" to "an encrypted web connection (https on port 443)"
- Quite simply, both are identical with one this exception: just after the TCP opening handshake has completed on TCP port 443, the client will send this plain-text to the server: "ClientHello".
- BTW, while many non-web email transfers are not encrypted, their authentication data transfers (username and password) usually are. The only difference here is the TCP port number.
- Anyway, with all SSL hand shakes, a valid server certificate must be present.
- A client will encrypt a message (to be sent to the server) by employing the public key found on the server's certificate. The server can only decrypt the key via the server's private key.
- A server will encrypt a message (to be sent to the client) by employing the server's private key. The client can only decrypt the key via the server's public key which is found on the server's certificate.
- Additional encryption is possible with a client certificate.
sequenceDiagram
    participant Client
    participant Server

    Note over Client,Server: TCP Handshake Completed

    Client->>Server: 1. ClientHello (Supported Cipher Suites, Random)
    Server->>Client: 2. ServerHello (Selected Cipher Suite, Random)
    Server->>Client: 3. Certificate (Server Public Key)
    Server->>Client: 4. ServerHelloDone

    Note over Client: Validates Certificate

    Client->>Server: 5. ClientKeyExchange (Encrypted Premaster Secret)
    Client->>Server: 6. ChangeCipherSpec (Switch to Encrypted)
    Client->>Server: 7. Finished (Finished Message - Encrypted)

    Server->>Client: 8. ChangeCipherSpec (Switch to Encrypted)
    Server->>Client: 9. Finished (Finished Message - Encrypted)

    Note over Client,Server: Secure Tunnel Established
    Client<->>Server: Encrypted Application Data
SSL/TLS cryptography is based upon:
- symmetric key cryptography (session keys)
- symmetric key algorithms both encrypt and decrypt data using a single key
- asymmetric key cryptography (e.g. public key cryptography)
- public key algorithms employ a pair of asymmetric keys which have a mathematical relationship to each other
- key-1 (also called the public key) is usually used by the client to "encrypt messages sent to the server" and "decrypt messages sent from the server"
- RSA: the public key is the product of two very large primes
- ECC: the public key contains both the "X" and "Y" parameters of an
algebraic equation for an elliptical curve (tutorial).
Caveat: ECC is currently implemented in two popular forms: ECDH which replaces Duffie-Helman and ECDSA which replaces RSA.
- key-2 (also called the private key) is usually used by the server to "encrypt messages sent to the client" and "decrypt messages sent from the client"
- RSA: the private key is one of two prime numbers used to generate the public key (the second prime is discarded)
- ECC: the private key contains the initialization points of an algebraic equation for an elliptical curve (tutorial)
- CAVEAT: I used the word usually because the trust is mostly only one-way (you, the client, wanted proof you were giving your credit card to the desired retailer; and the retailer only cared if your credit card was valid). But if the client ALSO has a certificate, or the connection is B2B (business-to-business) then the connection can be double-encrypted AND the client certificate can also be treated as a digital signature.
- asymmetric messaging is much more computationally expensive than symmetric messaging, so ...
- The initial SSL handshake begins with asymmetric keys which are primarily used to:
- conceal the handshake of the shared secret which produces the "symmetric key" (also known as the "session key")
- conceal the dialog where client and server agree on a particular cipher
- ensure that only the designated receiver can read the message via a server certificate
- optionally, ensure that the designated sender is who he claims to be (via a client certificate which:
- From this point on only the symmetric "session key" is used to encrypt/decrypt the channel data
quantum computer caveats:- if you worry that quantum computers might be used to break SSL encryption anytime soon, then know this: both SSL (1995) and OpenSSL (1998) hail from a time when 32-bit personal computers were not as powerful as 64-bit machines sold today, which is one reason why they they flop back to "symmetric key cryptography". One way to extend the useful life of 64-bit personal computers is to ditch "symmetric key cryptography" and do the whole transaction using "asymmetric keys (at least for financial transactions)". Another alternative would be to always require (the now optional) client verification. In the instance where the client does not have an officially created client side certificate (which would contain a client public key), the client software (e.g. browser) could be commanded to create a pair of client public-private keys on the fly as part of a pseudo fallback certificate. While this could never be used to ensure no man in the middle, double encryption (employing public keys from both server and client) is better than single encryption (only employing the public key from the server)
- with all the hype about quantum computers soon being able to solve the factoring problem associated with public key cryptography, you would think they have
made some progress. This 2025 article (https://www.theregister.com/2025/07/17/quantum_cryptanalysis_criticism/)
makes two interesting points:
- quantum computers at this point are nothing more than physics experiments
- while quantum computers can factor really small numbers, they can barely find the factors of 21 (which are 3 and 7; something any schoolchild can quickly solve)
- If Rational Quantum Mechanics ever becomes main stream, then quantum computers might never challenge current SSL cryptography.
- cryptographic hash functions
- message authentication codes (MAC)
- digital signatures
- Certificate
- is a public document which holds your public key
- if a leaf or server certificate, this document also contains the full URL of the host server
- it also holds the public key and URL of the intermediate certificate used to sign the leaf
- it must also contain a pair of date-stamps representing begin and end dates
- root certificates (which are used to sign intermediate certificates) are usually valid for 20-years
- intermediate certificates (which are used to sign leaf certificates) are usually valid for 10-years
- leaf certificates used to be only valid for 25-months. Starting on 2020-09-01 most vendors only issue certificates which will be valid for 398 days (~ 13 months). The additional time allows system admins to replace a certificate before it becomes invalid.
- the document must also contain a numeric hash which is used to prevent a man-in-the-middle attack where someone tries to change something on the certificate (in flight).
- If Bob wants to send to Alice (Eve is a potential eavesdropper)
- Bob acquires Alice's public certificate which contains Alice's public key (theory: this key is the product of two primes)
- Bob uses Alice's public key to encrypt the message then sends it to Alice
- Alice uses her private key to decrypt the message. Only she can do this (because she has never made it public).
*** stuff to keep you awake at night ***
Only she can do this in real time. But if you can make a T-connection, then...- Anyone with a supercomputer along with a database of "pre-computed primes" and "partial solutions" would be able to keep up in real-time (e.g. rather than attempt to factor a public key into its products in real-time, just do a look-up)
- Similarly, anyone "able to record the whole conversation" would (eventually) be able to read the message off-line using a traditional computer
- Anyone at a corporate firewall could keep up: https://www.bluecoat.com/inspect-your-ssl-traffic
- If Bob wants to send a message to Alice with proof it come from him (signing)
- Bob encrypts the message using his private key (only he can do this since his private key was never made public)
- Bob encrypts again using Alice's public key then sends to Alice
- Alice decrypts using her private key (only she can do this since her private key was never made public)
- Alice decrypts again using Bob's public key (message must have come from Bob because it was encrypted with Bob's private key)
- From this point on only the symmetric "session key" is used to encrypt/decrypt the channel data
Trusted Third Parties
- How does a client ensure that the designated server "is who he claims to be" and not "some man-in-the-middle" with a bogus/forged certificate?
- The server's certificate (which contains the server's public key) is issued by a trusted third party also called a certificate authority or CA
- The authority signs (encrypts) the server's certificate with the authority's private key which anyone can decrypt by obtaining the authority's public key from the
authority's certificate
- Think "government Issued passports" where you trust the passport holder based upon the reputation of the issuer
- Who signed the certificate authority's certificate? *** stuff to keep you awake at night ***
- In an ideal world, authority-x might sign for authority-y who might sign for authority-z (but this is not the usual behavior of competitors in a capitalistic marketplace)
- Many times, a large CA will employ a self-signed certificate (then you just say "I trust that authority"). Because of this limitation, self-signed CA certificates are not usually fetched from the internet. For example, the browser you are using to read this article might have several hundred certificates loaded into the root cache (BTW, many times a browser update will only be updating or deleting entries in this cache).
Nerd Stuff
Western conservatives are continually questioning the value of education (and theoretical research) then implementing austerity measures for the purpose of lowering taxes. [[[ BTW, this seems to happen more often in English-speaking countries; I have never seen my taxes ever go down ]]]. Between 2006 and 2015, Canadian conservatives attempted to defund all theoretical research in Canada claiming that Canada should only concentrate upon applied research. The NRC was partially defunded and scientists receiving any government money were muzzled. Pressure on academia is ten times worse under Donald Trump.
Most politicians would never click this next link which I placed here for all nerds: the modern RSA cryptographic system is based upon Fermat's Little Theorem first published in 1640.
The OpenSSL CLI (command line interpreter)
- to prove the underlying routines and libraries work properly (the developers of OpenSSL use this feature all the time)
- creating certificate signing requests (CSRs) along with the associated public and private keys, creating self-signed certificates, etc.
- Testing client-server connectivity
- can you connect at all?
- is there an SSL handshake after you connect?
- is there something wrong with the far-end server certificate?
- is the far-end server requesting a client certificate (this is usually optional) but would be an error if you have not defined one
- are near-end certificates usable?
- is your client trusted certificate chain usable?
- is a cipher missing?
- Browsers will hide error information only presenting an error icon. Using OpenSSL CLI as a test tool will present details for you to begin failure-mode analysis.
- Modern OpenVMS servers have no modern browsers so the OpenSSL CLI will be the only tool to get you out of most jams.
p.s. one of our systems sits behind a firewall with the server's IP address gen'd into a firewall ACL (Access Control List). If we wanted to use a PC to debug some weird connectivity problem we would need to unplug the server from the network then replace it with a properly configured PC. Since we run 24/7 this is not possible
- As a teaching tool
- use s_client to connect to Google or Twitter (they won't mind)
- use s_client to connect to your Apache web server
- Hacker Heaven: connect any two platforms end-to-end; one running s_server while the other running s_client
- if you are on a really tight budget, run the client and server sessions from two different command-line sessions on the same computer system
- click here for more details
- Proves that the underlying SSL library routines are functional (your SSL-based client software will link to the OpenSSL libraries; if the CLI programs work properly
and your client software does not, then the problem most likely exists in your code)
- As a tool to test client (or server) software you just wrote
- CLI source code, as well as the example programs, can be used to teach you how to write an SSL program (although s_server.c and s_client.c are in horrible shape; and whoever wrote s_client.c should be forced to endure the embarrassment of a public code review)
Official OpenSSL Documentation
- http://www.openssl.org/docs/
- http://www.openssl.org/docs/manpages.html
- http://www.openssl.org/docs/faq.html
Apps and Tools
- http://www.openssl.org/docs/apps/openssl.html (OpenSSL CLI)
- http://www.openssl.org/docs/apps/s_client.html (s_client specific help)
OpenSSL Documentation for Linux
| |
usual file locations | notes |
|---|---|---|
| program | /usr/bin/openssl /usr/bin/openssl3 |
the older stuff (eg. openssl-1.1.1k-17) the newer stuff (eg. openssl3-3.5.5-5) |
| config | /etc/pki/tls/openssl.cnf | always make a backup copy of this one |
| certificate(s) | /etc/pki/tls/certs | public certificates live here |
| key(s) | /etc/pki/tls/private | private keys live here |
Example 1: OpenSSL introductory stuff
Like most security software, OpenSSL seems deliberately unfriendly so you must read the official CLI docs
or poke around (er, hack).
Here is the command documentation for OpenSSL-3.5 (use the slider to change version-based help)
(1) typing "openssl" will always bring up the default package for your system
(2) on those systems supporting multiple packages, you may need type "openssl1" or "openssl3" to bring up alternative packages
(3) line switch "-help" and sub-commands "list" and "help" first appeared in 2016 with OpenSSL-1.1.0
(4) openssl stopped dropping into an interactive command mode in 2021 with OpenSSL-3.0.0 (so OpenSSL is now more of a "command interpreter" than a "command line interpreter")
Legend (for all my examples):
<sr>		= system response
<ur>		= user response
<enter>		= hit the enter key (in my newer examples this is "assumed")
<ctrl-c>	= hit "control c"
<ctrl-z>	= hit "control z"
<space>		= hit the space bar
<tab>		= hit the tab key
#		= start of comment in BASH (Linux/Unix)
\		= line continuation character in BASH (Linux/Unix)
!		= start of comment in DCL (OpenVMS)
-		= line continuation character in DCL (OpenVMS)
[prompt}	= my shell prompt
--------------------------------------------------------
<sr>	[prompt]
<ur>	openssl version
<sr>	OpenSSL 3.5.8 25 Aug 2026 (Library: OpenSSL 3.5.8 25 Aug 2026)
	[prompt]

<ur>	openssl help
<sr> 	...verbiage ensues...
	[prompt]
Example 2: (some) basic commands
================================================= NEW: begins with OpenSSL-1.1.0 (August 2016)
<ur>	openssl help list			#
<sr>	...verbiage ensues...
	[prompt]

<ur>	openssl list -standard-commands		# was: openssl list-standard-commands
<sr>	{ displays available commands }		#
	[prompt]				#

<ur>	openssl list -message-digest-commands	# was: openssl list-message-digest-commands
<sr>	{ displays available digests }		#
	[prompt]				#

<ur>	openssl list -cipher-commands		# was: openssl list-cipher-commands
<sr>	{ display available ciphers }		#
	[prompt]				#
================================================= common
<ur>	openssl no-rsa				# is rsa available?
<sr>	rsa					# yes, rsa is available
	[prompt]				#
<ur>	openssl help rsa			# NEW: display rsa specific help
	...verbiage ensues...			#
	[prompt]				#

<ur>	openssl no-dsa				# is dsa available?
<sr>	dsa					# yes, dsa is available
	[prompt]				#
<ur>	openssl help dsa			# NEW: display dsa specific help
	...verbiage ensues...			#
	[prompt]				#

<ur>	openssl no-ec				# is ec (elliptic key cryptography) available?
<sr>	ec					# yes, ec is available
	[prompt]				#
<ur>	openssl help ec				# NEW: display ec specific help
	...verbiage ensues...			#
	[prompt]				#

<ur>	openssl no-whatever			# is whatever available?
<sr>	no-whatever				# no, whatever us not available
	[prompt]				#
Example 3: delving deeper (what ciphers are available?)
<ur>	openssl list -cipher-commands		# new commands
<sr>	aes-128-cbc       aes-128-ecb       aes-192-cbc       aes-192-ecb
	...
	des-ede3-ofb      des3
	[prompt]

<ur>	openssl help ciphers
<sr>	...verbiage ensues...
	[prompt]

<ur>	openssl ciphers -tls1_3			#
<su>	...verbiage ensures...
	[prompt]
================================================ old commands (museum ware)
<ur>	openssl ciphers -?			#
<sr>	usage: ciphers args
	 -v	- verbose mode, a textual listing of the SSL/TLS ciphers in OpenSSL
	 -V	- even more verbose (OpenVMS users enter -"V" to preserve case)
	 -ssl2	- SSL2 mode
	 -ssl3	- SSL3 mode
	 -tls1	- TLS1 mode
	[prompt]

<ur>	openssl ciphers -ssl2			# display available ssl2 ciphers
<sr>	...verbiage ensues...			# might be an error message in 2014
	[prompt]				#

<ur>	openssl ciphers -ssl3			# display available ssl3 ciphers
<sr>	...verbiage ensues...			# might be an error message in 2020
	[prompt]				#

<ur>	openssl ciphers -tls1			# display available tls1 ciphers
<sr>	...verbiage ensues...			#
	[prompt]				#
================================================= common
<ur>	openssl ciphers -v			# display all available ciphers
<sr>	...verbiage ensues...			# 100 lines is typical
	[prompt]				#

<ur>	openssl ciphers -v | grep -i SSL	# display SSL stuff
<sr>	...verbiage ensues...			# 60 lines is typical
	[prompt]				#

<ur>	openssl ciphers -v | grep -i TLS	# display TLS-related stuff
<sr>	...verbiage ensues...			# 60 lines is typical
	[prompt]				#
OpenSSL CLI :: non-connection examples
1) This content of this section is more of an academic/pedagogical nature
2) Click skip this section if you are in a hurry to solve a connectivity problem
3) The following examples manipulate files rather than data streams but you will get the general idea
4) Anything typed into the OpenSSL CLI can also be called from the OpenSSL C-API
Cryptographic Exercises
exercise-01 "encrypt with base64"
=================================
<ur>	echo "These are the voyages of the starship Enterprise" > hack1a.txt	# use BASH to insert text into a file
<sr>	[prompt]								#

<ur>	cat hack1a.txt								# use BASH to test the file
<sr>	These are the voyages of the starship Enterprise
	[prompt]								#

<ur>	openssl help enc							#
<sr>	...verbiage ensues...
<ur>	openssl enc -base64 -in hack1a.txt					# encrypt using base64 (output to screen)
<sr>	VGhlc2UgYXJlIHRoZSB2b3lhZ2VzIG9mIHRoZSBzdGFyc2hpcCBFbnRlcnByaXNl
	Cg==
	[prompt]								#

<ur>	openssl enc -base64 -in hack1a.txt -out hack1b.txt			# encrypt using base64 (output to file)
<sr>	[prompt]								# no news is good news :-)

<ur>	openssl enc -base64 -d -in hack1b.txt					# now decrypt the file
<sr>	These are the voyages of the starship Enterprise			# success...
	[prompt]								#

Notes:
1) While "base64" is listed as a cipher (in older versions of openssl), it is not a form of secret encryption
   since it does not support the use of a secret key. But it does prove that this part of the CLI is working
   properly when "base64" is treated as a module.
2) OLDER VERSIONS: type "openssl list-cipher-commands" to see a list of ciphers offered by your installed product.
   Notice that the listing does include "base64"
3) NEWER VERSIONS: type "openssl ciphers -v" to see a list of ciphers offered by your installed product. However,
   may find this command more practical "openssl enc -ciphers"
   Notice that the listing does NOT include "base64" which is why you need the newer command switch "-base64"
4) One of the ciphers is "des3" which we will use in the next exercise
5) Newer versions of OpenSSL also include "base64" as a command to use in place of "enc -base64"
   Type "openssl help base64" for details.
exercise-02 "encrypt with des3"
===============================
<ur>	echo "To boldly go where no man has gone before" > hack2a.txt	# use BASH to insert text into a file
<sr>	[prompt]							#

<ur>	cat hack2a.txt							# use BASH to check the file
<sr>	To boldly go where no man has gone before			#
	[prompt]							#

<ur>	openssl help enc
<sr>	...verbiage ensues...
	[prompt]
<ur>	openssl enc -des3 -in hack2a.txt -out hack2b.bin		# encrypt file using des3 (output to file)
<sr>	enter des-ede3-cbc encryption password:				# prompting for a mandatory KEY
<ur>	secret789<enter>						# you will be typing this blind (no echo)
<sr>	Verifying - enter des-ede3-cbc encryption password:		# prompting for KEY verification
<ur>	secret789<enter>						# you will be typing this blind (no echo)
<sr>	[prompt]							# no news is good news :-)

<ur>	hexdump -C hack2b.bin						# more hacking (see note #4 below)
<sr>	00000000  53 61 6c 74 65 64 5f 5f  37 50 2d 64 5c bd 8b da  |Salted__7P-d\...|
	00000010  b7 74 bb bd 75 01 49 f5  b9 10 13 db fa 22 85 15  |.t..u.I......"..|
	00000020  1f 1f 25 94 08 23 d1 cb  2f d1 18 d8 7b 36 10 6c  |..%..#../...{6.l|
	00000030  9a de 91 d3 f6 7f b2 d5  46 3b 5e 7b 49 c1 29 ae  |........F;^{I.).|
	00000040
	[prompt]							#

<ur>	openssl enc -des3 -d -in hack2b.bin				# decrypt message file (out to screen)
<sr>	enter des-ede3-cbc decryption password:				#
<ur>	secret789<enter>						# you will be typing this blind (no echo)
<sr>	To boldly go where no man has gone before			# yay!
	[prompt]

<ur>	openssl enc -des3 -d -in hack2b.bin -k secret789		# decrypt without prompting
<sr>	To boldly go where no man has gone before
	[prompt]							#

<ur>	openssl enc -des3 -d -in hack2b.bin -k "secret789"		# double quotes work as well
<sr>	To boldly go where no man has gone before
	[prompt]							#

<ur>	echo "secret789" > hack2c.txt					# insert pass-phrase into file
<sr>	[prompt]							#

<ur>	openssl enc -des3 -d -in hack2b.bin -pass file:hack2c.txt	# decrypt (password from file)
<sr>	To boldly go where no man has gone before
	[prompt]							#

<ur>	openssl enc -des3 -d -in hack2b.bin -pass pass:secret789	# decrypt (inline password)
<sr>	To boldly go where no man has gone before
	[prompt]							#

Notes:
1) the "encryption password" is really a KEY which is used to both encrypt and decrypt
2) be very careful when you enter the pass phrase because some hidden characters (like <tab> and
   <space>) are processed as-is; for example, the following legal inputs produce different results
   a) secret789<space><enter>
   b) secret789<space><space><enter>
   c) <space>secret789<space><enter>
   d) <tab>secret789<space><enter>
   e) secret789<enter>
   f) <enter>
3) if you enter any double-quote characters at the interactive passphrase prompt they will be used to
   encrypt but it will be impossible to decrypt using the -k option which first strips quotes before
   processing
4) Notice the embedded phrase "Salted__" which is always present. Salt (randomized 64-bit data stored
   in the file) is combined with pepper (data not stored in the file (the pass phrase)) to cause every
   encryption of the same data to produce different results. This used to stop dictionary hacks. Try it
   yourself. Every time you type "openssl enc -des3" you will produce a different result. Now go back
   and store just a lower case 'a' as plain text then use a lower case 'a' as the pass phrase. The
   result will always contain 24-bytes.
5) Note: SALT is really a combination of the IV (Initialization Vector) and the key which is generated from the passphrase
*** And Now For a Little Theory ***

RSA Notes:
	0) https://en.wikipedia.org/wiki/RSA_(cryptosystem)
	1) RSA encryption/decryption is asymmetric and so requires two keys (one public, one private).
	2) RSA keys are based upon upon the product of two carefully chosen prime numbers.
	3) the private key is one of the primes.
	4) The public key is the product of two primes.
	5) during the initial handshake, the public key is passed in full view of the public (obviously).
	   (usually by reading the server's OpenSSL certificate)
	6) the client will use the server's public key to encrypt a message before transmission
	7) the server will use the server's private key to decrypt the received encrypted message
	8) Optional security: during the handshake, the server may ask the client to send a client public key.
	   The client will send it's client certificate (usually a user generated certificate) to the server.
	   The server will use the client's public key to send encrypted responses back to the client.
	   The client will use the client's private key to decrypt received responses.
	   This second scheme is known as digital signing.
	   CAVEAT: just to be clear, using the client's public and private keys to encrypt is done in addition
	   to using the server's public and private keys. The message is doubly encrypted.

RSA Data:
	d = private key
	n = public key
	e = 65537	(constant with RSA)
	c = m^e mod n	(formula for cipher text)
	m = c^d mod n	(formula for message text)
exercise-03 "create a new 32-bit private key file"
==================================================
Notes:
(1) 32 bits is too small for a certificate but (was) okay for this demo on primes
(2) on newer systems you may not use a key size lower than 512 bits (this limit will eventually increase)
(3) CAVEAT: confusingly, this private key file contains both "a 16-bit private key" AND "a 32-bit public key"

<sr>	[prompt]						# my BASH prompt
<ur>	openssl genrsa -out hack3a.key 32			# create a 32-bit public key
<sr>	Generating RSA private key, 32 bit long modulus
	.+++++++++++++++++++++++++++
	.+++++++++++++++++++++++++++
	e is 65537 (0x10001)
	[prompt]

<sr>	cat hack3a.key
<ur>	-----BEGIN PRIVATE KEY-----
	MIIBVAIBADANBgkqhkiG9w0BAQEFAASCAT4wggE6AgEAAkEAtJsdkqviXEtOq997
	...verbiage...
	BKaYCWHXezMAYLmDcJb3Sv47cfjBKQIgcQ8gAMaXvYb6D19m72Lefzyd9Sb7L9XU
	G5IKhoYJcFk=
	-----END PRIVATE KEY-----

<ur>	openssl rsa -in hack3a.key -text -noout			# interpret the key file
<sr>	Private-Key: (32 bit)					# private key file holds a 32-bit public key
	modulus: 4057358269 (0xf1d65fbd)			# this is the 32-bit public key
	publicExponent: 65537 (0x10001)				# same every time
	privateExponent: 1322158157 (0x4ece884d)
	prime1: 65123 (0xfe63)					# 16-bit prime1 (changes every genrsa)
	prime2: 62303 (0xf35f)					# 16-bit prime2 (changes every genrsa)
	exponent1: 51313 (0xc871)
	exponent2: 47415 (0xb937)
	coefficient: 60666 (0xecfa)
	[prompt]

Notes:
calc:	65123 x 62303 = 4057358269				# public key (product of two primes)

	[[[ display only the public key portion ]]]

<ur>	openssl pkey -in hack3a.key -outform PEM -pubout	# alias:  openssl rsa -in hack3a.key -outform PEM -pubout
<sr>	-----BEGIN PUBLIC KEY-----
	...verbiage...
	-----END PUBLIC KEY-----
	[prompt]
exercise-04 "create a new 512-bit private key file"
===================================================
Notes:
(1) 512 bits is too small for a certificate but is okay for this demo on primes
(2) A certificate publisher will not allow to to use anything smaller that 2048 bits. (this limit will eventually increase)
(3) CAVEAT: confusingly, this private key file contains both "a 256-bit private key" AND "a 512-bit public key"

<sr>	[prompt]						# my BASH prompt
<ur>	openssl genrsa -verbose -out hack4a.key 512		# 512 bits just for this demo
<sr>	Generating RSA private key, 512 bit long modulus
	......++++++++++++
	.....++++++++++++
	e is 65537 (0x10001)
	[prompt]

<ur>	cat hack4a.key						# view raw ASCII data
<sr>	-----BEGIN PRIVATE KEY-----
	MIIBVAIBADANBgkqhkiG9w0BAQEFAASCAT4wggE6AgEAAkEAvSPIB+9mim3FQ3T3
	Uhlmf19btGEXrDLICER+hQE5ZwpsIBCi8MVKGYJtUqkJjLW6LnjRrlce79Gq3Jy0
	qqYAnQIDAQABAkArFQtrQ0zIG1jjlLEBMmf2e3IYFEWgI7EMsQ1gnnbE0Wawaep9
	UGnTM4ko2VqaVC0qMdr08oOG/7tNXo+7w+rBAiEA3Wr0YpnrM6jZGjNliN0Fbiqw
	kEHFxJjmtXxK9qKtjyMCIQDarj2KBkU/z156+EISUiUOTm5xmVXw0CO3ak1m39kN
	PwIgVSz+xCuH0kCi+7RH2+WCYEXl1CipJp7XKXud7tDXyVcCIQCLplHuXurCQS9Y
	4ElxYbwAUt389asISiNE8kHTvIfkCQIgGPZ1NpJz7Me5tw3K/c+jP2uh0PN1Fx3s
	k7R4rqPqC/0=
	-----END PRIVATE KEY-----
	[prompt]

<ur>	openssl rsa -in hack4a.key -text -noout			# interpret the key file
<sr>	Private-Key: (512 bit, 2 primes)
	modulus:						# this is our 512-bit public key
	    00:bd:23:c8:07:ef:66:8a:6d:c5:43:74:f7:52:19:	# "00:" is just for padding
	    66:7f:5f:5b:b4:61:17:ac:32:c8:08:44:7e:85:01:
	    39:67:0a:6c:20:10:a2:f0:c5:4a:19:82:6d:52:a9:
	    09:8c:b5:ba:2e:78:d1:ae:57:1e:ef:d1:aa:dc:9c:
	    b4:aa:a6:00:9d					# 64 x 8 = 512 bits
	publicExponent: 65537 (0x10001)
	privateExponent:
	    2b:15:0b:6b:43:4c:c8:1b:58:e3:94:b1:01:32:67:
	    f6:7b:72:18:14:45:a0:23:b1:0c:b1:0d:60:9e:76:
	    c4:d1:66:b0:69:ea:7d:50:69:d3:33:89:28:d9:5a:
	    9a:54:2d:2a:31:da:f4:f2:83:86:ff:bb:4d:5e:8f:
	    bb:c3:ea:c1
	prime1:
	    00:dd:6a:f4:62:99:eb:33:a8:d9:1a:33:65:88:dd:	# "00:" is just for padding
	    05:6e:2a:b0:90:41:c5:c4:98:e6:b5:7c:4a:f6:a2:
	    ad:8f:23						# 32 x 8 = 256 bits
	prime2:
	    00:da:ae:3d:8a:06:45:3f:cf:5e:7a:f8:42:12:52:	# "00:" is just for padding
	    25:0e:4e:6e:71:99:55:f0:d0:23:b7:6a:4d:66:df:
	    d9:0d:3f						# 32 x 8 = 256 bits
	exponent1:
	    55:2c:fe:c4:2b:87:d2:40:a2:fb:b4:47:db:e5:82:
	    60:45:e5:d4:28:a9:26:9e:d7:29:7b:9d:ee:d0:d7:
	    c9:57
	exponent2:
	    00:8b:a6:51:ee:5e:ea:c2:41:2f:58:e0:49:71:61:
	    bc:00:52:dd:fc:f5:ab:08:4a:23:44:f2:41:d3:bc:
	    87:e4:09
	coefficient:
	    18:f6:75:36:92:73:ec:c7:b9:b7:0d:ca:fd:cf:a3:
	    3f:6b:a1:d0:f3:75:17:1d:ec:93:b4:78:ae:a3:ea:
	    0b:fd
	[prompt]

Notes:	prime1 x prime2 = modulus [[[ verified with python3 (see code just below) ]]]

	[[[ display only the public key portion ]]]

<ur>	openssl pkey -in hack4a.key -pubout
<sr>	-----BEGIN PUBLIC KEY-----
	MFwwDQYJKoZIhvcNAQEBBQADSwAwSAJBAL0jyAfvZoptxUN091IZZn9fW7RhF6wy
	yAhEfoUBOWcKbCAQovDFShmCbVKpCYy1ui540a5XHu/RqtyctKqmAJ0CAwEAAQ==
	-----END PUBLIC KEY-----

=====================================================================================
	[[[ python code ]]]

#!/usr/bin/python3
# ===============================================
# title  : hexhack.py
# author : Neil Rieck
# created: 2026-10-30
# command: ./hexhack.py
# purpose: show that 2 primes yield a public key
# ===============================================

def hexToInt(h):
    h = h.replace(":", "")
    i = int(h, 16)
    return i

def main():
    hex1 = ("00:dd:6a:f4:62:99:eb:33:a8:d9:1a:33:65:88:dd:"
            "05:6e:2a:b0:90:41:c5:c4:98:e6:b5:7c:4a:f6:a2:"
            "ad:8f:23")
    hex1
    int1 = hexToInt(hex1)
    print(f"1: {int1}")
    hex2 = ("00:da:ae:3d:8a:06:45:3f:cf:5e:7a:f8:42:12:52:"
            "25:0e:4e:6e:71:99:55:f0:d0:23:b7:6a:4d:66:df:"
            "d9:0d:3f")
    int2 = hexToInt(hex2)
    print(f"2: {int2}")
    hex3 = ("00:bd:23:c8:07:ef:66:8a:6d:c5:43:74:f7:52:19:"
            "66:7f:5f:5b:b4:61:17:ac:32:c8:08:44:7e:85:01:"
            "39:67:0a:6c:20:10:a2:f0:c5:4a:19:82:6d:52:a9:"
            "09:8c:b5:ba:2e:78:d1:ae:57:1e:ef:d1:aa:dc:9c:"
            "b4:aa:a6:00:9d")
    int3 = hexToInt(hex3)
    print(f"3: {int3}")
    int9 = int1 * int2
    print(f"T: {int1 * int2}")
    if int3 == int9:
        print("-i-public key matches computation")
    else:
        print("-e-public key does not match computation")
    print("adios.")
#
#   catch-all
#
if __name__ == '__main__':
    main()
#

[[[ test tun ]]]

$ ./hexhack.py
1: 100150112010161307879515856121031132306698659122001444898818934850356408848163
2: 98912057108083667072310118792931755799161095298663828215802679204755615059263
3: 9906053598530051227934063406761483703202138091076134197773187892479644785078437429264959035844067388603060925849342642737264890185245627610728542813683869
T: 9906053598530051227934063406761483703202138091076134197773187892479644785078437429264959035844067388603060925849342642737264890185245627610728542813683869
-i-public key matches computation
adios.
$
Certificate Exercises / Examples
exercise-05 "create a CSR (certificate signing request)"
========================================================
notes:	1) use the 512-bit key file created in exercise-04
	2) copy/use of file openssl.cnf is optional

<sr>	[prompt]						# my BASH prompt
<ur>	cp /etc/pki/tls/openssl.cnf	openssl.cnf		# copy template (OPTIONAL)
<sr>	[prompt]

<ur>	openssl req 		\
	 -new			\
	 -key hack4a.key	\
	 -out hack5b.csr	\
	 -config openssl.cnf					# OPTIONAL
<sr>	You are about to be asked to enter information that will be incorporated
	into your certificate request.
	What you are about to enter is what is called a Distinguished Name or a DN.
	There are quite a few fields but you can leave some blank
	For some fields there will be a default value,
	If you enter '.', the field will be left blank.
	-----
	Country Name (2 letter code) [XX]:CA			# my responses are in red
	State or Province Name (full name) []:Ontario		#
	Locality Name (eg, city) [Default City]:Waterloo	#
	Organization Name (eg, company) []:Neil Rieck		# I am not a business
	Organizational Unit Name (eg, section) []:Neil Rieck	#
	Common Name (eg, YOUR name) [server]:neilrieck.net	#
	Email Address []:n.rieck@bell.net
	Please enter the following 'extra' attributes
	to be sent with your certificate request
	A challenge password []:<enter>
	An optional company name []:<enter>
	[prompt]
<ur>	cat hack5b.csr						# view raw CSR data
<sr>	-----BEGIN CERTIFICATE REQUEST-----
	MIIBdDCCAR4CAQAwgbgxCzAJBgNVBAYTAkNBMRAwDgYDVQQIEwdPbnRhcmlvMREw
	DwYDVQQHEwhXYXRlcmxvbzElMCMGA1UEChMcVW5pdGVkIEZlZGVyYXRpb24gb2Yg
	UGxhbmV0czETMBEGA1UECxMKU3RhciBGbGVldDEZMBcGA1UEAxMQSmVhbi1MdWMg
	UGlja2FyZDEtMCsGCSqGSIb3DQEJARYeamVhbi1sdWMucGljYXJkQHN0YXItZmxl
	ZXQudWZwMFwwDQYJKoZIhvcNAQEBBQADSwAwSAJBAKIwjuJiJJalNN6uQYW+JAn2
	6uipqT8/VvDNIGhqJDxrI2wMj5sNcWn5MmQsZFdl/pxioQvlsdFb8Idk1ZsLc9kC
	AwEAAaAAMA0GCSqGSIb3DQEBBQUAA0EAILOaqUUSsb0vgTyXqUKsBi12mgSbsLgu
	rZEEyu0gSsTdVIkkwkVvhavYpxCENbCqiRxH+uHZLkYvbTTfmvUapA==
	-----END CERTIFICATE REQUEST-----
	[prompt]

<ur>	openssl req -noout -text -in hack5b.csr			# view interpreted CSR data
<sr>	Certificate Request:
	Data:
	Version: 0 (0x0)
	Subject:Subject: C=CA, ST=Ontario, L=Waterloo,
		O=Neil Rieck, OU=Neil Rieck,
		CN=neilrieck.net/emailAddress=n.rieck@bell.net
	Subject Public Key Info:
	Public Key Algorithm: rsaEncryption
	RSA Public Key: (512 bit)
	Modulus (512 bit):					# public key
	00:a2:30:8e:e2:62:24:96:a5:34:de:ae:41:85:be:		# "00:" is just padding
	24:09:f6:ea:e8:a9:a9:3f:3f:56:f0:cd:20:68:6a:
	24:3c:6b:23:6c:0c:8f:9b:0d:71:69:f9:32:64:2c:
	64:57:65:fe:9c:62:a1:0b:e5:b1:d1:5b:f0:87:64:
	d5:9b:0b:73:d9						# 64 x 8 = 512 bits
	Exponent: 65537 (0x10001)
	Attributes:
	a0:00
	Signature Algorithm: sha1WithRSAEncryption
	20:b3:9a:a9:45:12:b1:bd:2f:81:3c:97:a9:42:ac:06:2d:76:
	9a:04:9b:b0:b8:2e:ad:91:04:ca:ed:20:4a:c4:dd:54:89:24:
	c2:45:6f:85:ab:d8:a7:10:84:35:b0:aa:89:1c:47:fa:e1:d9:
	2e:46:2f:6d:34:df:9a:f5:1a:a4
	[prompt]
exercise-06 "create a self-signed certificate"
caveat: modern browsers reject these BUT can be used to test the OpenSSL CLI client
===================================================================================
notes:	1) use of file "openssl.cnf" is OPTIONAL
	2) x509 indicates "self signed"

<sr>	[prompt]
<ur>	openssl req		\
	 -new			\
	 -x509			\
	 -days 365		\
	 -set_serial 20160101	\
	 -key hack4a.key	\
	 -out hack6b.crt	\
	 -config openssl.cnf
<sr>	You are about to be asked to enter information that will be incorporated
	into your certificate request.
	What you are about to enter is what is called a Distinguished Name or a DN.
	There are quite a few fields but you can leave some blank
	For some fields there will be a default value,
	If you enter '.', the field will be left blank.
	-----
	Country Name (2 letter code) [AU]:CA			# my responses in RED (CA=Canada)
	State or Province Name (full name) []:Ontario		# Canada has provinces
	Locality Name (eg, city) [Default City]:Waterloo
	Organization Name (eg, company) []:Neil Rieck		# I am not a business
	Organizational Unit Name (eg, section) []:Neil Rieck
	Common Name (eg, YOUR name) [server]:neilrieck.net	#
	Email Address []:n.rieck@bell.net			#
	[prompt]
<ur>	openssl x509 -in hack6b.crt -text -noout		# let's see it (processed)
<sr>	Certificate:
	    Data:
	        Version: 3 (0x2)
	        Serial Number: 20160101 (0x1339e65)
	        Signature Algorithm: sha1WithRSAEncryption
	        Issuer: C=CA, ST=Ontario, L=Waterloo,
			O=Neil Rieck,
			OU=Neil Rieck,
			CN=neilrieck.net/emailAddress=n.rieck@bell.net
	        Validity
	            Not Before: Jan  1 21:06:15 2016 GMT
	            Not After : Dec 31 21:06:15 2016 GMT
	        Subject: C=CA, ST=Ontario, L=Waterloo,
			O=Neil Rieck,
			OU=Neil Rieck,
			CN=neilrieck.net/emailAddress=n.rieck@bell.net
	        Subject Public Key Info:
	            Public Key Algorithm: rsaEncryption
	            RSA Public Key: (512 bit)
	                Modulus (512 bit):
	                    00:a2:30:8e:e2:62:24:96:a5:34:de:ae:41:85:be:
	                    24:09:f6:ea:e8:a9:a9:3f:3f:56:f0:cd:20:68:6a:
	                    24:3c:6b:23:6c:0c:8f:9b:0d:71:69:f9:32:64:2c:
	                    64:57:65:fe:9c:62:a1:0b:e5:b1:d1:5b:f0:87:64:
	                    d5:9b:0b:73:d9
	                Exponent: 65537 (0x10001)
	        X509v3 extensions:
	            X509v3 Subject Key Identifier:
	                83:79:4A:B8:D5:ED:C4:C5:58:A8:4B:0F:07:E6:8B:FB:A3:22:19:9C
	            X509v3 Authority Key Identifier:
	                keyid:83:79:4A:B8:D5:ED:C4:C5:58:A8:4B:0F:07:E6:8B:FB:A3:22:19:9C
	                DirName:/C=CA/ST=Ontario/L=Waterloo
				/O=United Federation of Planets
				/OU=Star Fleet
				/CN=neilrieck.net/emailAddress=n.rieck@bell.net
	                serial:01:33:9E:65

	            X509v3 Basic Constraints:
	                CA:TRUE
	    Signature Algorithm: sha1WithRSAEncryption
	        08:36:67:15:01:c4:8c:e6:2d:10:de:ed:bb:13:4f:cb:9d:4f:
	        9a:c9:8b:61:ee:84:16:e8:9b:0f:db:a5:05:c7:d5:94:e6:9b:
	        b1:0f:40:d5:bc:be:09:75:5e:7a:33:46:f7:3a:4c:c2:8b:61:
	        c2:85:ad:a0:f2:cf:00:d2:e1:0d
	[prompt]
<ur>	cat hack6b.crt						# let's see it (raw)
<sr>	<...hex dump...>					#
exercise-7 "certificates: compound operations, private companies AND development platforms"
===========================================================================================
Note: a private CA (certificate authority) is sometimes required for development platdforms
operations:
1) create your own CA (certificate authority) key
2) create your own CA (certificate authority) certificate with v3 extensions
3) create your own CSR (certificate signing request) with v3 extensions
4) use your own CA certificate to sign the CSR with v3 extensions
=====================================================================
coming soon (it works on my server)
	-or-
follow the steps documented here:
    https://www.feistyduck.com/library/openssl-cookbook/
    Starts on page 39 of the free PDF
Elliptical-Curve Cryptography
- https://en.wikipedia.org/wiki/Elliptic-curve_cryptography
- This technology involves the use of a private key which is used to (computationally) traverse an algebraic curve to generate a public key.
- It is virtually impossible to work backwards (convert the public key to the primary key)
- Since this technology does not involve factoring a public key (which is the product of two prime numbers), it might be able to evade quantum computers.
- CAVEAT: It appears that EC keys are ten times smaller than RSA keys
exercise-8 "generate an EC key"
CAVEAT: as with RSA, this private key file actually contains both private and public keys
========================================
<ur>	openssl help ec			# show help
<sr>	...verbiage ensues...
	[prompt]
<ur>	openssl ecparam -list_curves	# show available curves
<sr>	...verbiage ensues...
	[prompt]
======================================== generate a new private-public pair (method-1)
<ur>	openssl genpkey -algorithm EC -pkeyopt ec_paramgen_curve:prime256v1 -out ec_private.pem
<sr>	[prompt]
======================================== generate a new private-public pair (method-2)
<ur>	openssl ecparam -name prime256v1 -genkey -out ec_private.pem
<sr>	[prompt]
======================================== look inside private file
<ur>	openssl ec -in ec_private.pem -text
<sr>	read EC key
	Private-Key: (256 bit)
	priv:
	    b6:28:6d:69:65:24:fa:45:04:e9:c0:3e:43:90:ed:
	    9a:a9:71:91:00:67:6b:a4:b6:1a:25:34:a0:fb:1d:
	    ce:d8
	pub:
	    04:fa:71:89:42:dd:ef:b2:1a:f5:40:04:52:ca:0e:
	    85:ef:4e:93:a5:2e:63:79:80:c7:9a:31:b5:34:0c:
	    06:16:d2:a0:62:24:88:f5:1e:33:4e:ec:af:ad:a1:
	    ea:07:1a:90:8f:d1:b9:aa:1e:75:62:8c:83:99:42:
	    d4:b7:be:04:55
	ASN1 OID: prime256v1
	NIST CURVE: P-256
	writing EC key
	-----BEGIN EC PRIVATE KEY-----
	MHcCAQEEILYobWllJPpFBOnAPkOQ7ZqpcZEAZ2uktholNKD7Hc7YoAoGCCqGSM49
	AwEHoUQDQgAE+nGJQt3vshr1QARSyg6F706TpS5jeYDHmjG1NAwGFtKgYiSI9R4z
	TuyvraHqBxqQj9G5qh51YoyDmULUt74EVQ==
	-----END EC PRIVATE KEY-----
	[prompt]
======================================== extract public key
<ur>	openssl ec -in ec_private.pem -pubout -out ec_public.pem
<sr>	[prompt]

########################################################################
EC Cheat Sheet:
==============
# show available curves
openssl ecparam -list_curves

# generate a new private key file for a curve
# method-1:
openssl ecparam -name prime256v1 -genkey -out private-key.pem
# method-2:
openssl genpkey -algorithm EC -pkeyopt ec_paramgen_curve:prime256v1 -out private-key.pem

# extract the corresponding public key
openssl ec -in private-key.pem -pubout -out public-key.pem

# optional: create a self-signed certificate
openssl req -new -x509 -key private-key.pem -out cert.pem -days 360

# optional: convert pem to pfx
openssl pkcs12 -export -inkey private-key.pem -in cert.pem -out cert.pfx

#######################################################################
Digging Deeper (for math nerds)
==============

<ur>	openssl ecparam -out ec_param.pem -name prime256v1 -param_enc explicit
<sr>	[prompt]
<ur>	openssl ecparam -in ec_param.pem  -text
<sr>	EC-Parameters: (256 bit)
	Field Type: prime-field
	Prime:
	    00:ff:ff:ff:ff:00:00:00:01:00:00:00:00:00:00:
	    00:00:00:00:00:00:ff:ff:ff:ff:ff:ff:ff:ff:ff:
	    ff:ff:ff
	A:
	    00:ff:ff:ff:ff:00:00:00:01:00:00:00:00:00:00:
	    00:00:00:00:00:00:ff:ff:ff:ff:ff:ff:ff:ff:ff:
	    ff:ff:fc
	B:
	    5a:c6:35:d8:aa:3a:93:e7:b3:eb:bd:55:76:98:86:
	    bc:65:1d:06:b0:cc:53:b0:f6:3b:ce:3c:3e:27:d2:
	    60:4b
	Generator (uncompressed):
	    04:6b:17:d1:f2:e1:2c:42:47:f8:bc:e6:e5:63:a4:
	    40:f2:77:03:7d:81:2d:eb:33:a0:f4:a1:39:45:d8:
	    98:c2:96:4f:e3:42:e2:fe:1a:7f:9b:8e:e7:eb:4a:
	    7c:0f:9e:16:2b:ce:33:57:6b:31:5e:ce:cb:b6:40:
	    68:37:bf:51:f5
	Order:
	    00:ff:ff:ff:ff:00:00:00:00:ff:ff:ff:ff:ff:ff:
	    ff:ff:bc:e6:fa:ad:a7:17:9e:84:f3:b9:ca:c2:fc:
	    63:25:51
	Cofactor:  1 (0x1)
	Seed:
	    c4:9d:36:08:86:e7:04:93:6a:66:78:e1:13:9d:26:
	    b7:81:9f:7e:90
	-----BEGIN EC PARAMETERS-----
	MIH3AgEBMCwGByqGSM49AQECIQD/////AAAAAQAAAAAAAAAAAAAAAP//////////
	/////zBbBCD/////AAAAAQAAAAAAAAAAAAAAAP///////////////AQgWsY12Ko6
	k+ez671VdpiGvGUdBrDMU7D2O848PifSYEsDFQDEnTYIhucEk2pmeOETnSa3gZ9+
	kARBBGsX0fLhLEJH+Lzm5WOkQPJ3A32BLeszoPShOUXYmMKWT+NC4v4af5uO5+tK
	fA+eFivOM1drMV7Oy7ZAaDe/UfUCIQD/////AAAAAP//////////vOb6racXnoTz
	ucrC/GMlUQIBAQ==
	-----END EC PARAMETERS-----
	[prompt]
OpenSSL CLI :: connection examples
Using "openssl s_client" to connect to public sites
Notes:
- the following examples are for machines directly connected to the internet. Firewalls and proxy servers present additional challenges
- if the following commands do not work on your OpenVMS system then read this caveat
- if the following command fails with "400 Bad Request" from your Linux command line, you may need to use the optional switch "-crlf" (only valid with s_client) which will translate hitting your enter key into <cr><lf> (a.k.a. "\r" and "\n")
- here we use ssl3 because it is much more lenient than any version of tls
caveat: most web sites disabled support for ssl3 in 2014 (see: POODLE)
========================================================================= NEW: begins with OpenSSL-1.1.0 (August 2016)
<sr>	[prompt]							#
<ur>	openssl help s_client						#
	...verbiage ensues...						#
	[prompt]							# my BASH prompt
======================================================================== common
<ur>	openssl s_client -connect www.twitter.com:443 -tls1 -crlf	# connect to Twitter
									#
<sr>	...handshake verbiage...						# bla...bla...bla...
	---								# your s_client prompt
<ur>	GET / HTTP/1.0<enter>						# get default document; use HTTP 1.0
	host: www.twitter.com:443<enter>				# the host line was optional with HTTP/1.0 but is now required
	<enter>								# signal end of HTTP header
<sr>	HTTP/1.0 200 OK							# response
	Date: Fri, 22 Jun 2012 23:16:38 GMT				#
	Status: 200 OK							#
	Pragma: no-cache						#
	Content-Type: text/html; charset=UTF-8				#
Connecting to Google USA (non-USA sites may be redirected)
<sr>	[prompt]							#
<ur>	openssl s_client -connect www.google.com:443 -tls1 -crlf	# connect to Google USA
									#
<sr>	...handshake verbiage...						# bla...bla...bla...
	---								# your s_client prompt
<ur>	GET / HTTP/1.0<enter>						# get default document; use HTTP 1.0
	host: www.google.com:443<enter>					# the host line was optional with HTTP/1.0 but is now required
	<enter>								# signal end of HTTP header
<sr>	HTTP/1.0 302 Found						# 302 = moved
	Location: https://www.google.ca/				# so redirect to Canada
	Cache-Control: private
	Content-Type: text/html; charset=UTF-8
	Set-Cookie: expires=; expires=Mon, 01-Jan-1990 00:00:00 GMT; path=/; domain=www.google.com
Connecting to Google Canada (non-Canadian sites will be redirected)
<sr>	[prompt]							#
<ur>	openssl s_client -connect www.google.ca:443 -tls1 - crlf	# connect to Google Canada
									#
	...handshake verbiage...						# bla...bla...bla...
	---								# your s_client prompt
<ur>	GET / HTTP/1.1<enter>						# okay so let's try HTTP/1.1
	host: www.google.ca:443<enter>					# a desired host is needed for use with HTTP/1.1
	<enter>								# signal end of HTTP header
<sr>	HTTP/1.1 200 OK							#
	Set-Cookie: NID=61=H7WfG9OQ6uHDvVU8OJyt_Z4x8a4cj0DUpLUfH9D9eeKVou1FwaP8ok16
	vDlgV3sX1JPzrd3G8tNc3mDgbdPZy8mGnmpKJ3WCKHVT6gbCV8Z56rKIVgXokgJkptJZ-i00;
	expires=Sat, 22-Dec-2012 22:51:17 GMT; path=/; domain=.google.ca; HttpOnly
	Date: Fri, 22 Jun 2012 22:51:17 GMT
	Expires: -1
	Cache-Control: private, max-age=0
	Content-Type: text/html; charset=windows-1252
	Set-Cookie: PREF=ID=3ba285f540771657:FF=0:TM=1340405477:LM=1340405477:S=TpABG903GxV7Ufhg;
		expires=Sun, 22-Jun-2014 22:51:17 GMT; path=/; domain=.google.ca
	Set-Cookie: NID=61=H7WfG9OQ6uHDvVU8OJyt_Z4x8a4cj0DUpLUfH9D9eeKVou1FwaP8ok16vDlgV3sX1JPzrd
		3G8tNc3mDgbdPZy8mGnmpKJ3WCKHVT6gbCV8Z56rKIVgXokgJkptJZ-i00;
		expires=Sat, 22-Dec-2012 22:51:17 GMT; path=/; domain=.google.ca; HttpOnly
	P3P: CP="This is not a P3P policy! See http://www.google.com/support/accounts
		/bin/answer.py?hl=en&answer=151657 for more info."
	Server: gws
	X-XSS-Protection: 1; mode=block
	X-Frame-Options: SAMEORIGIN
	Transfer-Encoding: chunked

	1000								# byte count of chunked data block
	[...snip...]
Using 'openssl s_client' to connect to my Apache webserver (I/P=142.180.221.226 port=443)
Three connect commands (responses not shown)
<ur>	openssl s_client -connect 142.180.221.226:443 -h		# get help (only with OpenSSL-3)
------------------------------------------------------------------------
<ur>	openssl s_client -connect 142.180.221.226:443 -msg		# show the protocol handshake

<ur>	openssl s_client -connect 142.180.221.226:443 -showcerts	# what far-end certificates are available?

<ur>	openssl s_client -connect 142.180.221.226:443 -debug		# show more info hex and ASCII

<ur>	openssl s_client -connect 142.180.221.226:443 -state		# show ssl state transitions

Note: after anyone of the above commands, type the following:

<ur>	GET / HTTP/1.0<enter>						# get default document using HTTP/1.0
     	<enter>								# signal end of HTTP header
									# if this fails with "400 Bad Request" then try the connect command with optional switch: -crlf
Four connect commands (responses not shown)
click: quick steps for a series of complete steps near the bottom of this page
for optional client verification (where client=user)

<ur>	openssl s_client -connect 142.180.221.226:443	\
	 -cert client.crt				\
	 -key  client.key		<enter>

<ur>	openssl s_client -connect 142.180.221.226:443	\
		-cert client.pem	<enter>			# key + crt (both inside of pem file)

for optional client verification (where client=your system)

<ur>	openssl s_client -connect 142.180.221.226:443	\
		-cert /etc/pki/tls/certs/server.crt	\
		-key  /etc/pki/tls/private/server.key	\
		-tls1			<enter>			# only use TLS1 encryption

Note: after anyone of the above commands, type the following:

<ur> GET / HTTP/1.0<enter>						# get default document using HTTP/1.0
     <enter>								# signal end of HTTP header
									# if this did not work, then restart the whole command with the optional "-crlf" switch
Using 'openssl s_client' to connect to SSL$SIMPLE_SERV.C (I/P=142.180.39.15 port=5555)
Five connect commands (responses not shown)
<ur>	openssl s_client -connect 142.180.39.15:5555 -debug		# details while negotiating

<ur>	openssl s_client -connect 142.180.39.15:5555 -state		# watch SSL change states

<ur>	openssl s_client -connect 142.180.39.15:5555 -tls1 -debug	# use the TLS1 protocol

<ur>	openssl s_client -connect 142.180.39.15:5555 -ssl3 -debug	# use the SSL3 protocol

<ur>	openssl s_client -connect 142.180.39.15:5555			#					\
		-cert    client/client.pem				# PEM files require a HASH file		\
		-CAfile  client/client_ca.pem				# list of trusted certificates		\
		-CApath  client						#
OpenSSL client-server examples
Notes:- the client and server programs do not need to reside on different platforms but it is more fun if they do (two PCs also work)
- when connecting to the same machine use address "127.0.0.1" except in the case of the TLS protocol which contains additional security (with TLS just use the fully qualified domain name)
- Note: on the BASH shell
- lines ending with a dash are continued on the next line
- an exclamation is used to start a comment
- click here for instructions on how to do this experiment on Windows
A simple web server (cannot serve up a file)
Server:

<ur>	openssl s_server -accept 4433			\
		-cert   /etc/pki/tls/certs/server.crt	\
		-key    /etc/pki/tls/private/server.key	\
		-CAfile /etc/pki/tls/certs/chain.crt	\
		-debug					\
		-www							# barely simulate a webserver (lower case)
<sr>	Using default temp DH parameters
	Using default temp ECDH parameters
	ACCEPT

Client:

<ur>	openssl s_client -connect 142.180.39.15:4433 -debug		# will connect to server
<sr>	...handshake verbiage...						# bla...bla...bla...
<ur>	GET / HTTP/1.0<enter>						# request default page containing stats
	<enter>								# signal end of HTTP header
A web server (can serve up a file)
Server:

<ur>	cd								# run these tests from your home directory
<sr>	[prompt]							#

<ur>	echo "this is sample text" > neil.txt		<enter>		# create a small text file
<sr>	[prompt]							#

<ur>	openssl s_server -accept 4433			\
		-cert   /etc/pki/tls/certs/server.crt	\
		-key    /etc/pki/tls/private/server.key	\
		-CAfile /etc/pki/tls/certs/chain.crt	\
		-debug					\
		-WWW					<enter>		# simulate a better webserver (upper case)
<sr>	Using default temp DH parameters
	Using default temp ECDH parameters
	ACCEPT

Client:

<ur>	openssl s_client -connect 142.180.39.15:4433	\
		-cert vms_cert_dir/client.crt		\
		-key vms_cert_dir/client.key		<enter>		# will connect to server
<sr>	...handshake verbiage...						# bla...bla...bla...
<ur>	GET /neil.txt HTTP/1.0<enter>					# request file "neil.txt"
	<enter>								# signal end of HTTP header
<sr>	HTTP 200 (OK)
	...header verbiage...

	this is sample text						# presto
Web server with certificate-based client verification (popular in B2B applications)
- here I am showing a client presenting his own per-client certificate but in some B2B applications the client software will present the certificate of the local web server
- high level view of proof (only used during the initial handshake):
- remember that the client employs the server's public key when sending encrypted messages to the server. The server uses a private key to decrypt the message. If this works then the client can assume that the server is who he claims to be
- but if client-verification is requested, the client will begin encrypting messages using the client's private key which is then encrypted a second time using the server's public key before being sent. The server will use the server's private key on the first decrypt followed by the client's public key on the second decrypt. If this works then the server can assume that the client is who he claims to be (a.k.a. digital signing)
Server:

<ur>	cd								# run these tests from your home directory
<sr>	[prompt]

<ur>	cat neil.txt							# make sure test file exists
<sr>	this is sample text
	[prompt]							#

<ur>	openssl s_server -accept 4433			\
		-cert /etc/pki/tls/certs/server.crt	\
		-key  /etc/pki/tls/private/server.key	\
		-debug					\
		-WWW					\
		-Verify 9				<enter>		# force client to require a certificate
<sr>	verify depth is 9, must return a certificate
	Using default temp DH parameters
	Using default temp ECDH parameters
	ACCEPT

Client:

<ur>	openssl s_client -connect 142.180.39.15:4433	\
		-cert vms_cert_dir/client.crt		\
		-key vms_cert_dir/client.key		<enter>		# will connect to server
<sr>	...handshake verbiage...						# bla...bla...bla...
<ur>	GET /neil.txt HTTP/1.0<enter>					# request file "neil.txt"
	<enter>								# signal end of HTTP header
<sr>	HTTP 200 (OK)
	...header verbiage...

	this is sample text						# presto
<ur>	openssl s_client -connect 142.180.39.15:4433			# reconnect "without any certs"
<sr>	CONNECTED(00000005)
	depth=0 /C=CA/ST=ON/L=KITCHENER/O=BELL CANADA/OU=BELL-ATS/CN=www.bellics.com/emailAddress=neil@bellics.com
	verify error:num=18:self signed certificate			# this is not really an error
	verify return:1
	depth=0 /C=CA/ST=ON/L=KITCHENER/O=BELL CANADA/OU=BELL-ATS/CN=www.bellics.com/emailAddress=neil@bellics.com
	verify return:1
	262761:error:14094410:SSL routines:SSL3_READ_BYTES:sslv3 alert handshake failure:S3_PKT:1102:SSL alert number 40
	262761:error:140790E5:SSL routines:SSL23_WRITE:ssl handshake failure:S23_LIB:182:

Server:

<sr>	...verbiage...
	261215:error:140890C7:SSL routines:SSL3_GET_CLIENT_CERTIFICATE:peer did not return a certificate:S3_SRVR:2611:
	ACCEPT								# waiting for another transaction
Example 7: OpenSSL advanced stuff
<sr>	$									# my BASH prompt
<ur>	openssl ciphers								# see available local ciphers
<sr>	DHE-RSA-AES256-SHA:DHE-DSS-AES256-SHA:AES256-SHA:DHE-RSA-CAMELLIA256-SHA:
	DHE-DSS-CAMELLIA256-SHA:CAMELLIA256-SHA:EDH-RSA-DES-CBC3-SHA:EDH-DSS-DES-
	CBC3-SHA:DES-CBC3-SHA:DES-CBC3-MD5:DHE-RSA-AES128-SHA:DHE-DSS-AES128-SHA:
	AES128-SHA:DHE-RSA-SEED-SHA:DHE-DSS-SEED-SHA:SEED-SHA:DHE-RSA-CAMELLIA128
	-SHA:DHE-DSS-CAMELLIA128-SHA:CAMELLIA128-SHA:RC2-CBC-MD5:DHE-DSS-RC4-SHA:
	RC4-SHA:RC4-MD5:RC4-MD5:EXP1024-DHE-DSS-DES-CBC-SHA:EXP1024-DES-CBC-SHA:E
	DH-RSA-DES-CBC-SHA:EDH-DSS-DES-CBC-SHA:DES-CBC-SHA:DES-CBC-MD5:EXP1024-DH
	E-DSS-RC4-SHA:EXP1024-RC4-SHA:EXP-EDH-RSA-DES-CBC-SHA:EXP-EDH-DSS-DES-CBC
	-SHA:EXP-DES-CBC-SHA:EXP-RC2-CBC-MD5:EXP-RC2-CBC-MD5:EXP-RC4-MD5:EXP-RC4-
	MD5
	$
<ur>	openssl s_client -connect www.google.ca:443 -cipher "RC4-SHA"		# connect using the RED cipher
	...handshake verbiage...							# bla...bla...bla...

note:	the requested cipher might not be available at the far end
Creating/using a trusted client chain (add remote cert to local cache)
This first example demonstrates connecting to a system which employs self-signed certificatesnotes: 1) I am on my production node "KAWC96" connecting to my development node "KAWC09" 2) We could just ignore the error 18 then continue 3) Or save the remote certificate in a local repository ---------------------------------------------------------------------------------------- <sr> [prompt] # my BASH prompt <ur> cd # start in home location <sr> [prompt] # <ur> openssl s_client -connect kawc09.on.bell.ca:443 -state -showcerts # connect to development platform # (without any local certificate) <sr> CONNECTED(00000005) SSL_connect:before/connect initialization SSL_connect:SSLv2/v3 write client hello A SSL_connect:SSLv3 read server hello A depth=0 /C=ca/ST=Ontario/L=Kitchener/O=Bell Canada/OU=Bell-ATS/CN=kawc09.on.bell.ca/emailAddress=neil@kawc09.on.bell.ca verify error:num=18:self signed certificate <<<--- oops (let's fix this) verify return:1 depth=0 /C=ca/ST=Ontario/L=Kitchener/O=Bell Canada/OU=Bell-ATS/CN=kawc09.on.bell.ca/emailAddress=neil@kawc09.on.bell.ca verify return:1 SSL_connect:SSLv3 read server certificate A SSL_connect:SSLv3 read server key exchange A SSL_connect:SSLv3 read server done A SSL_connect:SSLv3 write client key exchange A SSL_connect:SSLv3 write change cipher spec A SSL_connect:SSLv3 write finished A SSL_connect:SSLv3 flush data SSL_connect:SSLv3 read finished A --- Certificate chain 0 s:/C=ca/ST=Ontario/L=Kitchener/O=Bell Canada/OU=Bell-ATS/CN=kawc09.on.bell.ca/emailAddress=neil@kawc09.on.bell.ca i:/C=ca/ST=Ontario/L=Kitchener/O=Bell Canada/OU=Bell-ATS/CN=kawc09.on.bell.ca/emailAddress=neil@kawc09.on.bell.ca --- Server certificate -----BEGIN CERTIFICATE----- MIICtzCCAiACCQCOJDXcN8BI4TANBgkqhkiG9w0BAQUFADCBnzELMAkGA1UEBhMC [...snip...] S/To2pITuhif+f7Mec4qU/SDUXpj6Se/tJE9TjE2Mc5edTUmgX3amMpYUnQwBHti zQb9M8XXRU0RwBHZgqOYk/amVFeVCVFxw9jn -----END CERTIFICATE----- subject=/C=ca/ST=Ontario/L=Kitchener/O=Bell Canada/OU=Bell-ATS/CN=kawc09.on.bell.ca/emailAddress=neil@kawc09.on.bell.ca issuer=/C=ca/ST=Ontario/L=Kitchener/O=Bell Canada/OU=Bell-ATS/CN=kawc09.on.bell.ca/emailAddress=neil@kawc09.on.bell.ca --- No client certificate CA names sent --- SSL handshake has read 1270 bytes and written 361 bytes --- New, TLSv1/SSLv3, Cipher is DHE-RSA-AES256-SHA Server public key is 1024 bit Secure Renegotiation IS supported Compression: NONE Expansion: NONE SSL-Session: Protocol : TLSv1 Cipher : DHE-RSA-AES256-SHA Session-ID: DE5C43E6C8B445FCDA60894A08650E5B19D1E99DAF3F70D2661EE60956001CF1 Session-ID-ctx: Master-Key: CFF329BE8FFF7B8FD7E6201B16F1AC3663EFF5633CDDD6EA52C79ED4A5C1A7A1F796DECCD77FCD21D497DC2021402118 Key-Arg : None Start Time: 1343864769 Timeout : 300 (sec) Verify return code: 18 (self signed certificate) <<<---oops (let's fix this) --- <ur> <ctrl-Y> # we're done so hit <ctrl-Y> <sr> INTERRUPT $
Create a trusted chain (or add to an existing chain)
Note: This is similar to what happens when you import a certificate into your browser
<ur>	cre xxx_kawc09.crt								# create a file
	-----BEGIN CERTIFICATE-----							# past in the remote certificate from above
	MIICtzCCAiACCQCOJDXcN8BI4TANBgkqhkiG9w0BAQUFADCBnzELMAkGA1UEBhMC
	[...snip...]
	S/To2pITuhif+f7Mec4qU/SDUXpj6Se/tJE9TjE2Mc5edTUmgX3amMpYUnQwBHti
	zQb9M8XXRU0RwBHZgqOYk/amVFeVCVFxw9jn
	-----END CERTIFICATE-----
	<ctrl-z>									# hit <ctrl-z> to exit file-creation with SAVE
<sr>	Exit
	$
<ur>	copy xxx_kawc09.crt vms_cert_dir						# optional: copy file to our cert directory
<sr>	$
<ur>	set def vms_cert_dir								# now move over there
<sr>	$
<ur>	dir client_ca.pem								# any chains like this here?
<sr>	%DIRECT-W-NOFILES, no files found						# nope
<ur>	copy xxx_kawc09.crt client_ca.pem						# copy cert into new PEM
		or									# or
	copy client_ca.pem, xxx_kawc09.crt client_ca.pem				# append cert onto existing PEM
<sr>	$
<ur>	openssl x509 -hash -noout -in client_ca.PEM					# compute hash of pem
<sr>	1132507a									# this is the computed result
<ur>	copy client_ca.PEM 1132507a.0							# create a hash file with '.0' extension
<sr>	$
<ur>	openssl verify "-CApath" vms_cert_dir -verbose -purpose any client_ca.PEM	# test the PEM-hash combo
<sr>	client_ca.pem: OK								# looks good so far
<ur>	set def sys$login:								# back to our home directory
<sr>	$
<ur>	openssl s_client -connect kawc09.on.bell.ca:443 -state	-			# connect to development platform (again)
		-cert vms_cert_dir/kawc96.crt			-			#
		-key vms_cert_dir/kawc96.key			-			#
		-"CAfile" vms_cert_dir/client_ca.PEM					# but reference trusted cert chain
<sr>	CONNECTED(00000005)
	SSL_connect:before/connect initialization
	SSL_connect:SSLv2/v3 write client hello A
	SSL_connect:SSLv3 read server hello A
	depth=0 /C=ca/ST=Ontario/L=Kitchener/O=Bell Canada/OU=Bell-ATS/CN=kawc09.on.bell.ca/emailAddress=neil@kawc09.on.bell.ca
	verify return:1									<<<--- cool (fixed)
	SSL_connect:SSLv3 read server certificate A
	SSL_connect:SSLv3 read server key exchange A
	SSL_connect:SSLv3 read server done A
	SSL_connect:SSLv3 write client key exchange A
	SSL_connect:SSLv3 write change cipher spec A
	SSL_connect:SSLv3 write finished A
	SSL_connect:SSLv3 flush data
	SSL_connect:SSLv3 read finished A
	---
	Certificate chain
	0 s:/C=ca/ST=Ontario/L=Kitchener/O=Bell Canada/OU=Bell-ATS/CN=kawc09.on.bell.ca/emailAddress=neil@kawc09.on.bell.ca
	i:/C=ca/ST=Ontario/L=Kitchener/O=Bell Canada/OU=Bell-ATS/CN=kawc09.on.bell.ca/emailAddress=neil@kawc09.on.bell.ca
	---
	Server certificate
	-----BEGIN CERTIFICATE-----
	MIICtzCCAiACCQCOJDXcN8BI4TANBgkqhkiG9w0BAQUFADCBnzELMAkGA1UEBhMC
	[...snip...]
	S/To2pITuhif+f7Mec4qU/SDUXpj6Se/tJE9TjE2Mc5edTUmgX3amMpYUnQwBHti
	zQb9M8XXRU0RwBHZgqOYk/amVFeVCVFxw9jn
	-----END CERTIFICATE-----
	subject=/C=ca/ST=Ontario/L=Kitchener/O=Bell Canada/OU=Bell-ATS/CN=kawc09.on.bell.ca/emailAddress=neil@kawc09.on.bell.ca
	issuer=/C=ca/ST=Ontario/L=Kitchener/O=Bell Canada/OU=Bell-ATS/CN=kawc09.on.bell.ca/emailAddress=neil@kawc09.on.bell.ca
	---
	No client certificate CA names sent
	---
	SSL handshake has read 1270 bytes and written 361 bytes
	---
	New, TLSv1/SSLv3, Cipher is DHE-RSA-AES256-SHA
	Server public key is 1024 bit
	Secure Renegotiation IS supported
	Compression: NONE
	Expansion: NONE
	SSL-Session:
	Protocol : TLSv1
	Cipher : DHE-RSA-AES256-SHA
	Session-ID: 96B7F72BDCCB65C8040BD1DFE714989D87F966D000AB7ED9CDD9AEF5FD4EAE89
	Session-ID-ctx:
	Master-Key: 7737874E462FAFD277E6541BD2608070BEBB15393D6897125F1DF8A10AC3AE24D5FD65BA0F909F9576A04856345BB6EE
	Key-Arg : None
	Start Time: 1343865022
	Timeout : 300 (sec)
	Verify return code: 0 (ok)					<<<---cool (fixed)
	---
<ur>	<ctrl-z>									# we are done
<sr>	Exit
	$
Overview of obtaining Signed Certificates
Overview:
- The main objective here is to create a CSR (Certificate Signing Request). This activity will generate two files:
- whatever.key
- holds the "private key" which you will never divulge to anyone
- never encrypt this file. If you do then you will be prompted for a password whenever you restart Apache
- whatever.csr
- holds certificate details about you and your sever including your "public key".
- you will display the raw file on you side before copying-then-pasting into a window at your certificate authority's web site
- whatever.key
- Once you have paid your money, and the Certificate Authority is convinced you are not attempting to generate a certificate for someone else's fully-qualified-domain,
they will generate two files (some authorities will email files to you while others will send you an email instructing you on how to retrieve them from their site)
- whatever.crt (this is your public certificate; it was made by signing whatever.csr)
- vendor.crt
this is the vendor's public certificate which was used to sign whatever.crt
-OR-
a chain of intermediate files from their CA-Root certificate down to, but not including your certificate
OpenSSL CLI commands for the annual ritual
note: this is a real-world example for server: kawc96.on.bell.ca
      (substitute numerical values for ccyymmdd)

commands:
1) openssl genrsa   -out kawc96_ccyymmdd.key 2048
2) openssl req -new -key kawc96_ccyymmdd.key -out kawc96_ccyymmdd.csr
3) openssl req -noout -text -in                   kawc96_ccyymmdd.csr
4) cat (on Unix/Linux)                            kawc96_ccyymmdd.csr
	or
   type (on OpenVMS)                              kawc96_ccyymmdd.csr

steps:
1) copy/paste the contents into the submission window at your certificate vendor's site
2) the vendor will sign your CSR then will hand it back to you as a CRT in base-64 format
   (they used to do that by email; but all modern services now require you to fetch it)
3) save it as a file of the form:		  kawc96_ccyymmdd.crt
4) visit the vendor's site to get a copy the certificate they used to sign your CSR.
   (sometimes these are presented as a chain file of intermediate certificates)
   I saved mine as: kawc96_ccyymmdd_vendor.crt
5) modify the Apache config file "ssl.conf" (see steps above)
   kawc96_ccyymmdd.key        (private key which will never been shared with anyone)
   kawc96_ccyymmdd.crt        (public certificate which contains your public key)
   kawc96_ccyymmss_vendor.crt (vendor's public certificate used to sign your cert)
6) restart the server (checking your log files)
A little more hacking (er, self education)
OpenSSL CLI commands to display the certificate files just for the fun of it

 1) openssl x509 -noout -text -in kawc96_ccyymmdd.crt
 2) openssl x509 -noout -text -in kawc96_ccyymmdd_vendor.crt
 3) openssl rsa  -noout -text -in kawc96_ccyymmdd.key
Creating multi-host CSRs in 2025
I have been using multi-host certificates for over two decades, and ordering them was simple until 2025.
- You first create a regular CSR then produce an ASCII dump.
- Now you surf over to your desired Certificate Authority (CA) vendor then indicate your desire to purchase a multi-host certificate.
- When prompted, you paste you ASCII dump into the desired text box.
- Next, you are prompted for additional host names
Starting in 2025, the procedure above did not produce a multi-host certificate(???).
After contacting the vendor, a non-technical specialist cast the blame on me for not including the additional hosts in the CSR (so why was I still being prompted for a
list of additional hosts?)
Click here to see my hack which worked.
Testing/Retesting
- Your certificate vendor will provide access to post installation tools which will verify the certificate installation as well as test your Apache-based OpenSSL engine.
- It would be wise to test your site every few months to ensure you are not offering to use ciphers or protocols which are no longer considered secure
- Here is one publicly available tool for testing your site right now: https://www.ssllabs.com/ssltest/
- Caveat: you may not be able to use vendor-provided tools if your server is sitting on a private intranet behind a firewall. Also, some of the cheaper vendors
do not provide any tools.
In most instances, the server admin person will test the new certificates by connecting with a modern browser like Chrome or MS-Edge. However, these browsers come with a large collection of CA Root certificates which means that (sometimes) you will only have browser connectivity while connecting by other methods will fail since a leaf-to-root certification path cannot be made. This exact thing happened to me recently when I updated both my CER and KEY files but neglected to update my chain file (of intermediate certificates) from the previous year. Why was this failing now? My host provider changed certificate vendors which meant that my chain was no longer valid). Anyway, here is the python script I used to detect, then fix, this problem: server_certificate_check
openssl s_server (quick steps)
step 1: create file "index.html" in your local folder
=====================================================
<html>
<head>
<title>index.html</title>
</head>
<body>
<p>this is a fake index file used for testing via the openssl cli</p>
</body>
</html>

step 2: create local certificates
=================================
step 2a: create a key
   openssl genrsa -des3 -out server.key 2048	# requires a passphrase
   -or-
   openssl genrsa       -out server.key 2048	# no passphrase
step 2b: create a CSR
   openssl req -key server.key -new -out server.csr
--------------------------------------------------- dialog start
You are about to be asked to enter information that will be incorporated
into your certificate request.
What you are about to enter is what is called a Distinguished Name or a DN.
There are quite a few fields but you can leave some blank
For some fields there will be a default value,
If you enter '.', the field will be left blank.
-----
Country Name (2 letter code) [XX]:CA
State or Province Name (full name) []:Ontario
Locality Name (eg, city) [Default City]:Kitchener
Organization Name (eg, company) [Default Company Ltd]:Bell-ATS
Organizational Unit Name (eg, section) []:Bell-ATS
Common Name (eg, your name or your server's hostname) []:bfdc0d.on.bell.ca
Email Address []:neil.rieck@bell.ca

Please enter the following 'extra' attributes
to be sent with your certificate request
A challenge password []:
An optional company name []:
--------------------------------------------------- dialog stop
step 2c: self-sign the csr
  openssl x509 -signkey server.key -in server.csr -req -days 365 -out server.crt

step-3: start the server (self-signed)
======================================
openssl s_server -accept 443	\
	-debug -WWW		\
	-cert ./server.crt	\
	-key  ./server.key

possible reasons for failure
============================
1) port not opened in your firewall
2) Apache already listening on port 443

Test from the same platform or another
======================================
openssl s_client -connect bfdc0d.on.bell.ca:443

GET /index.html HTTP/1.0<enter><enter>
web page verbiage is returned
expert hacks
step-4: create a self-signed Root CA (to sign your own cert)
============================================================
openssl req -x509 -sha256	\
  -days 1825			\
  -newkey rsa:2048		\
  -keyout ccyymmdd_root-CA.key	\
  -out    ccyymmdd_root-CA.crt
----------------------------------------------------------- dialog start
Generating a 2048 bit RSA private key
..........................................................+++
...+++
writing new private key to 'ccyymmdd_root-CA.key'
Enter PEM pass phrase:neil
Verifying - Enter PEM pass phrase:neil
-----
You are about to be asked to enter information that will be incorporated
into your certificate request.
What you are about to enter is what is called a Distinguished Name or a DN.
There are quite a few fields but you can leave some blank
For some fields there will be a default value,
If you enter '.', the field will be left blank.
-----
Country Name (2 letter code) [XX]:CA
State or Province Name (full name) []:Ontario
Locality Name (eg, city) [Default City]:Kitchener
Organization Name (eg, company) [Default Company Ltd]:Bell-ATS
Organizational Unit Name (eg, section) []:Bell-ATS
Common Name (eg, your name or your server's hostname) []:neilrieck
Email Address []:neil.rieck@bell.ca
----------------------------------------------------------- dialog stop

step-5: use your root-CA cert to sign your original csr
        note: new cert will be named domain2.crt
=======================================================
step-51: create a config file (domain.ext) with the following content:
         note: DNS.1 is required; other DNS entries are optional
----------------------------------------------------------- content start
authorityKeyIdentifier=keyid,issuer
basicConstraints=CA:FALSE
subjectAltName = @alt_names

[alt_names]
DNS.1 = bfdc0d.on.bell.ca
DNS.2 = bfdc0e.on.bell.ca
----------------------------------------------------------- content stop
step-52: sign your original csr
openssl x509 -req		\
  -CA      ccyymmdd_root-CA.crt	\
  -CAkey   ccyymmdd_root-CA.key	\
  -in      domain.csr		\
  -out     domain2.crt		\
  -days    365			\
  -CAcreateserial		\
  -extfile domain.ext
----------------------------------------------------------- dialog start
Signature ok
subject=/C=CA/ST=Ontario/L=Kitchener/O=Bell-ATS/OU=Bell-ATS
	/CN=bfdc0d.on.bell.ca/emailAddress=neil.rieck@bell.ca
Getting CA Private Key
Enter pass phrase for ccyymmdd_root-CA.key:neil
[prompt ~]

step-53: display the cert
=========================
  openssl x509 -noout -text -in domain2.crt

step-54: start the server (signed cert)
=======================================
openssl s_server -accept 443	\
  -debug -WWW			\
  -cert ./server.crt		\
  -key  ./server.key		\
  -CAcert ./ccyymmdd_root-CA.crt
Local Links
External Links
Free OpenSSL books
- https://www.feistyduck.com/library/openssl-cookbook/
- https://www.feistyduck.com/books/apache-security/
OpenSSL for OpenVMS
- http://polarhome.com/openssl/ - they have both binary file (smaller) and source file (larger) versions.
Okay so every time I connect to this Swedish hacker site I think about "The Girl With the Dragon Tattoo" by Stieg Larsson
SSL (general)
- http://www.openssl.org/ (the industry-wide home of OpenSSL)
- https://en.wikipedia.org/wiki/Transport_Layer_Security (a.k.a. SSL/TLS)
- http://luxsci.com/blog/ssl-versus-tls-whats-the-difference.html
- http://technet.microsoft.com/en-us/library/cc781800(v=ws.10).aspx (SSL/TLS in Windows Server 2003)
- https://en.wikipedia.org/wiki/Public_key_infrastructure (a.k.a. PKI)
- https://en.wikipedia.org/wiki/X.509 (a.k.a. X.509)
- http://tools.ietf.org/html/rfc5246 (a.k.a. rfc-5246)
- http://www.debian-administration.org/articles/618 - Certificate Authority (CA) with OpenSSL
- https://www.feistyduck.com/books/openssl-cookbook/ OpenSSL Cookbook every ssl enthusiast needs to read this
OpenSSL Tutorials
- http://users.dcc.uchile.cl/~pcamacho/tutorial/crypto/openssl/openssl_intro.html Save this one to your hard drive
- https://www.digitalocean.com/community/tutorials/openssl-essentials-working-with-ssl-certificates-private-keys-and-csrs
- because many times you can learn more by connecting to an UNIX/Linux/OpenVMS server from your PC
- If you only have one server platform then you have no other choice
- In a pinch, you can put two PCs back-to-back (type "openssl s_server" on one, type "openssl c_client" on the other)
- In a real pinch you can run server and client on the same machine but it's not really the same
- http://www.slproweb.com/products/Win32OpenSSL.html - very high quality work from Shining Light Productions; please donate a few bucks if you can
- http://gnuwin32.sourceforge.net/packages/openssl.htm
 Back to Home
Neil Rieck
Waterloo, Ontario, Canada.